Typosquatting: how a small variation in your domain can put your brand at risk
October 8, 2026 | Iñigo de las Heras Nuin
Protección de MarcaCibersecurity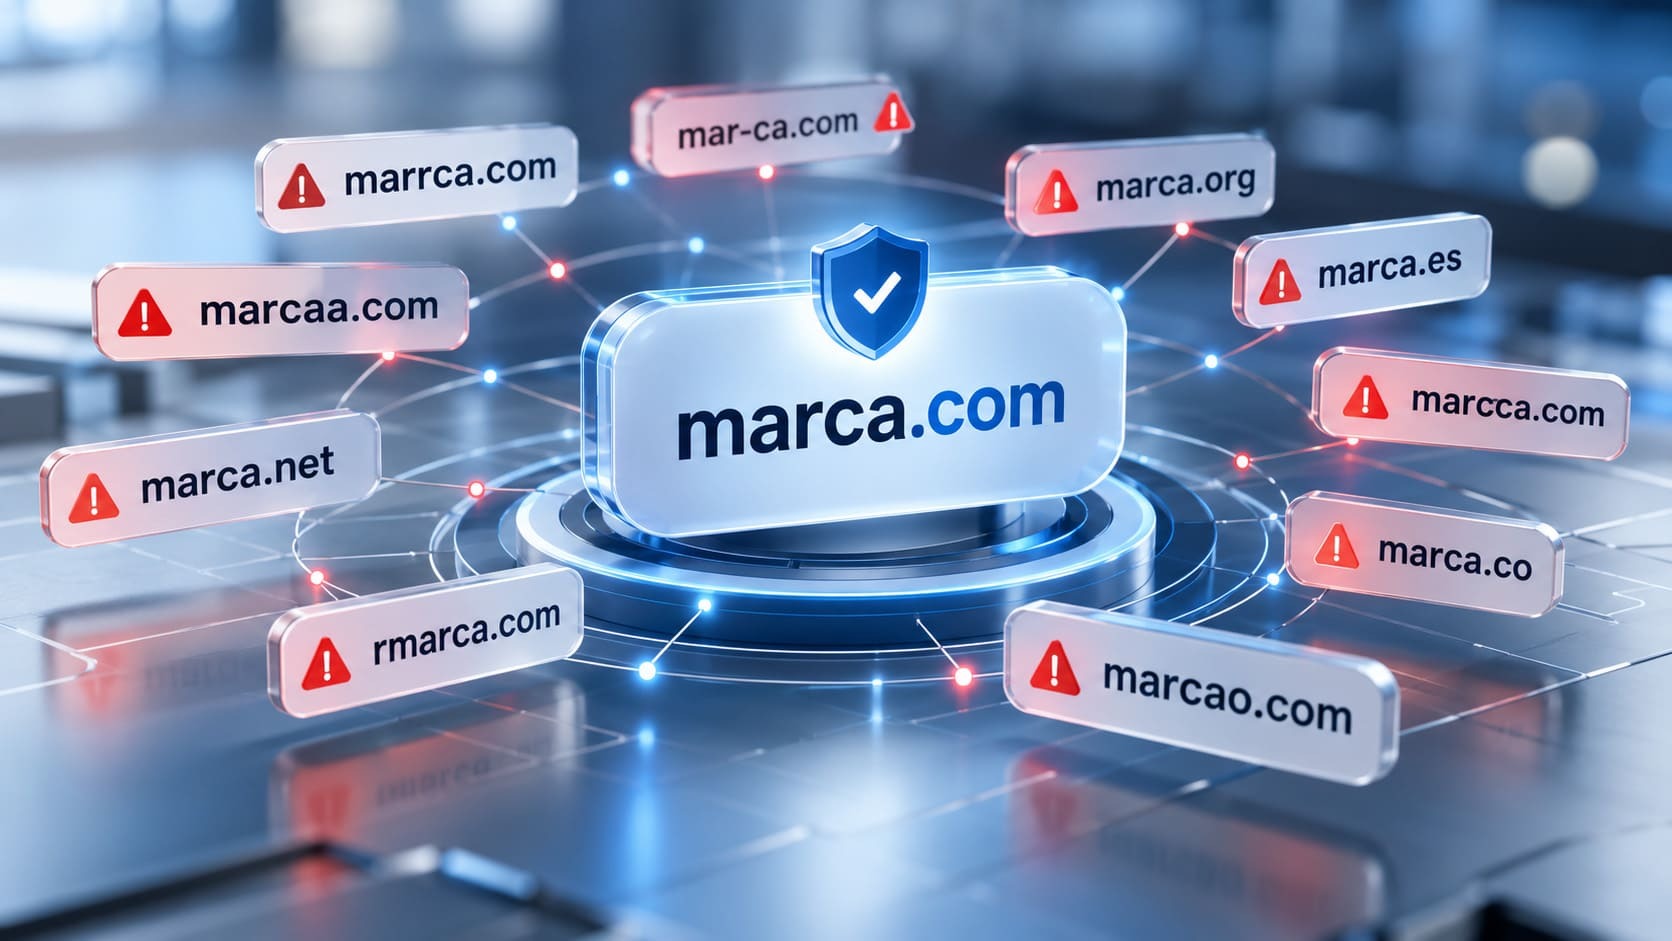
Mistyping a web address may seem like a minor mistake.
An extra letter, the wrong key, a hyphen that should not be there or a different extension. Normally, the user simply corrects the error and carries on browsing.
The problem starts when someone has already registered that similar-looking domain.
In that case, a small mistake can take the user to a completely different website that imitates a company’s identity, attempts to obtain credentials, displays advertising, redirects traffic to another service or is even used to send emails that appear to come from the legitimate brand.
This practice is known as typosquatting, and it shows why protecting a brand online involves more than simply registering its main domain.
What is typosquatting?
Typosquatting involves registering domains that deliberately resemble the domain of a well-known company, brand or service by exploiting small variations that may go unnoticed.
The aim is to benefit from the similarity between the two domains.
For example, if a company uses company.com, a third party could try to register variations based on common typing mistakes, additional letters, hyphens or changes to the extension.
To the brand owner, these domains may look clearly different.
To a user who sees them quickly in an email, an advert, a message or on a mobile screen, the difference may be far less obvious.
And it is precisely this confusion that can turn the technique into a security and brand protection problem.
A typing mistake can be enough
One of the simplest techniques is to anticipate common typing errors.
When we type quickly, it is easy to swap two letters, leave one out, duplicate one or press a nearby key.
An attacker can register some of these variations in the hope that users will reach them by mistake.
But typosquatting does not rely only on accidental errors.
The domain can also be used deliberately in phishing campaigns, fraudulent messages or links designed so that the user does not stop to check every character before clicking.
The better known a brand is and the more users interact with it, the more opportunities there may be to exploit this kind of confusion.
Duplicated, removed or swapped letters
Many typosquatting variations are extremely simple.
A letter may disappear from the original name, appear twice or swap position with the next one.
Nearby keyboard letters can also be used to create domains that still look very similar to the legitimate one.
The problem is that we do not usually analyse a web address character by character.
Our brain recognises the overall brand name and, if the domain looks right at first glance, it is easy to continue browsing without noticing the difference.
This similarity becomes even more relevant when the domain appears inside an email link or is viewed on a mobile device, where there is less space to display the full address.
A hyphen can also create a different domain
Adding a hyphen is another simple way to create a variation.
If a company uses brandname.com, someone could register a version such as brand-name.com.
Terms that create an appearance of legitimacy can also be added: words related to support, customers, payments, access, shop or security.
In these cases, we are not necessarily dealing with a simple typing mistake, but the principle is similar: creating a domain that is close enough to the original identity for the user to trust it.
That is why, when analysing possible risks around a brand, it is important not to focus exclusively on the most obvious spelling mistakes.
Similar-looking characters can also cause confusion
Some cases are even harder to detect visually.
Certain characters can look very similar depending on the typeface being used. One letter may be replaced by another that looks almost identical, or characters from other alphabets may be used that closely resemble Latin characters at first glance.
These techniques are commonly known as homograph attacks.
To a user, the domain may appear practically identical to the legitimate one even though it is technically different.
This is one of the reasons why quickly checking a brand name in a URL is not always enough to determine whether you are really on its official website.
Changing the extension can also create a false sense of legitimacy
The part after the name also matters.
A company may operate primarily with a .com, but that does not prevent someone else from registering the same name under another available extension.
Depending on the context, a user may interpret that domain as an alternative website, an international version, a shop or a specific service belonging to the same company.
The existence of hundreds of different extensions makes it unrealistic to register every possible combination around a brand.
That is why protection does not necessarily mean accumulating domains.
It means identifying which extensions and variations present a genuine risk based on the brand’s visibility, the markets it operates in, its activity and the way customers interact with it.
What can a similar-looking domain be used for?
Registering a similar domain does not automatically mean fraudulent activity is taking place.
There may be legitimate coincidences, particularly where generic terms or brands containing common words are involved.
The risk appears when the domain deliberately tries to take advantage of another organisation’s identity or reputation.
One of the best-known uses is phishing.
A similar domain can host a page that imitates a real website in an attempt to obtain usernames, passwords, banking information or other sensitive data.
But there are other possibilities.
The domain may redirect users to another company, display advertising, attempt to sell counterfeit products, imitate an official online shop or be used as the basis for fraudulent emails.
In other cases, the aim may simply be to capture part of the traffic that should have reached the legitimate domain.
Email is also part of the risk
One of the more serious consequences of typosquatting appears when the domain is used to create email accounts.
An address based on a visually similar variation can be used to impersonate a supplier, an employee, a finance department or a company manager.
In a long email conversation, a tiny difference in the domain can easily go unnoticed.
This makes it possible to use similar domains as part of impersonation attacks targeting employees, customers, distributors or suppliers.
For this reason, domain monitoring should not only look at whether a website has been published.
An apparently empty domain may still be useful for fraudulent activity through email or other services.
Should every possible variation of a brand be registered?
Trying to register every possible spelling mistake, extension and imaginable combination is rarely a realistic strategy.
The number of variations can be enormous.
And not all of them present the same level of risk.
A more reasonable protection strategy is to identify which ones are most likely to cause confusion.
For example, it may make sense to consider particularly obvious typing errors, variations that are very close to the main domain, extensions that are relevant to the company’s market or combinations that could be especially attractive for an impersonation campaign.
Defensive registration can form part of this strategy, but it should not be the only measure.
Monitoring helps detect what you cannot register
Even if a company protects the most important variations of its domain, there will always be combinations that remain unregistered.
That is why the other part of the strategy involves monitoring which domains appear around the brand.
Detecting a similar registration does not necessarily mean immediate action is required.
The first step is to analyse who is using it, what it is being used for and whether there is a genuine risk of confusion, fraud or infringement.
Monitoring makes it possible to carry out this follow-up and detect registrations that could otherwise go unnoticed until a customer, supplier or employee encounters the problem.
The earlier a potential threat is identified, the more time there is to analyse it and decide how to respond.
Protecting the main domain is only the beginning
Registering a company’s main domain is essential, but it does not prevent third parties from registering other similar variations.
Typosquatting exploits precisely this space around the brand: spelling mistakes, small modifications, alternative extensions or combinations that appear legitimate enough to inspire trust.
That is why a digital brand protection strategy should combine different measures.
Defensively registering the most relevant domains can reduce certain risks, while monitoring can help detect new variations that appear over time.
At Entorno Digital, we can help companies analyse their domain portfolio, identify variations that may represent a risk and monitor potential registrations that attempt to take advantage of their digital identity.
Because online, a single letter can separate your company’s domain from a website created to impersonate it.